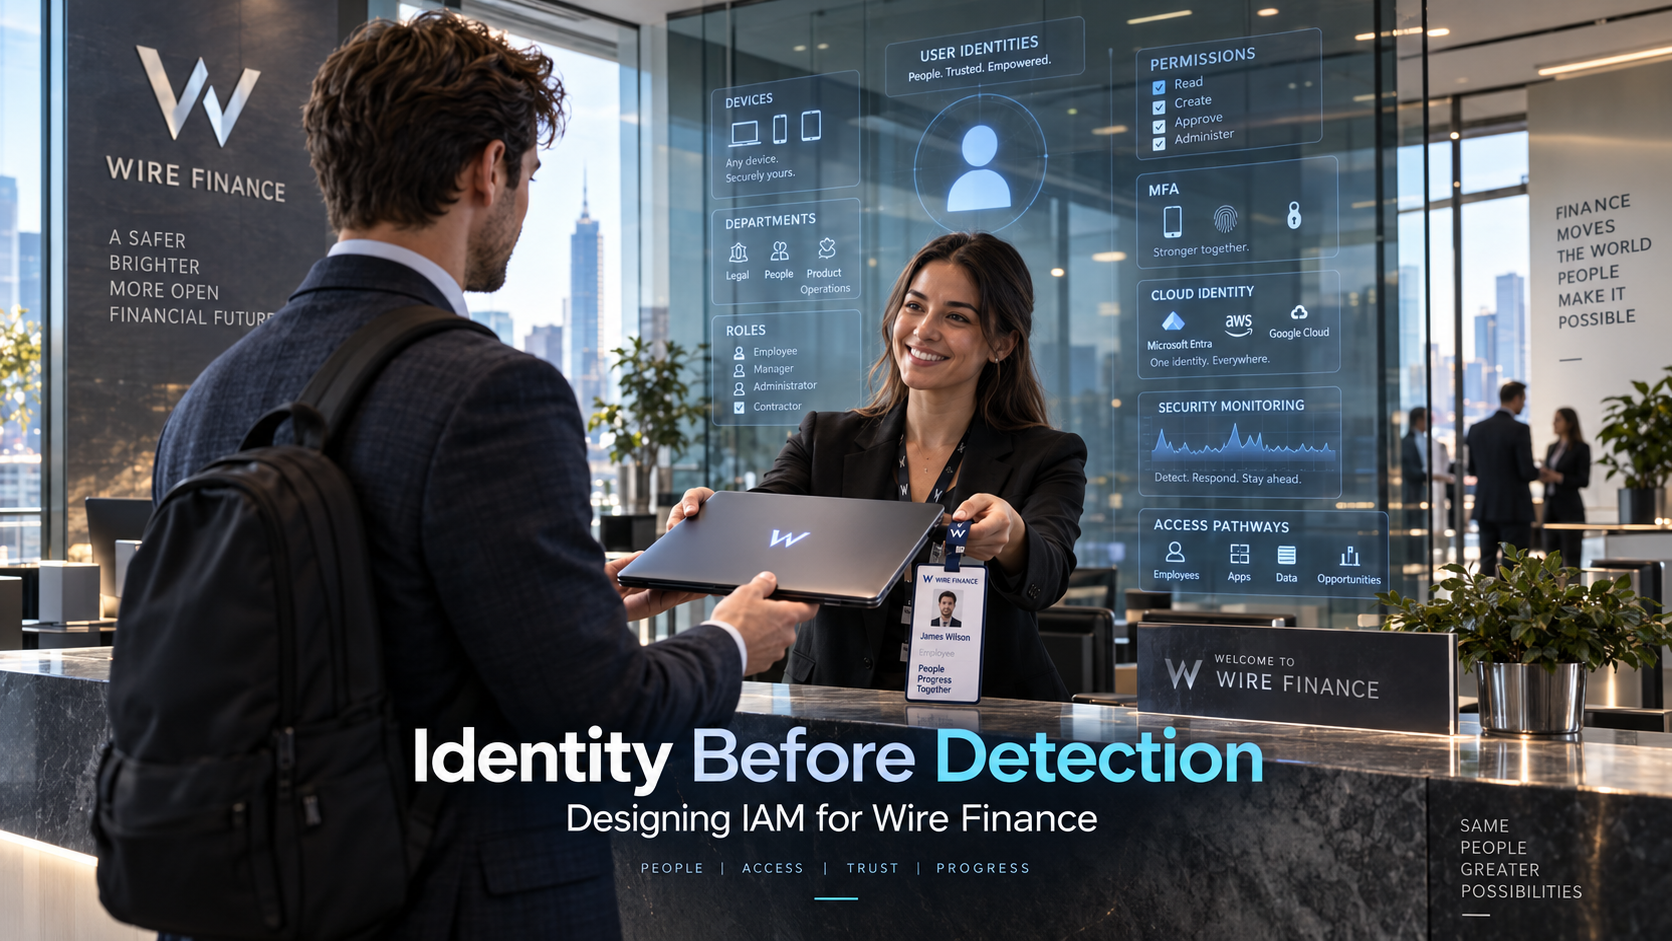
Introduction
Have you ever wondered how everything seems to work so smoothly when you join a new organisation?
You arrive on your first day, you’re handed a company device, given your login details, and somehow the organisation already seems to know who you are, where you belong, and what you should have access to. It can feel a little like college: your name is already on the register before you’ve even figured out how the system behind it works.
But behind that seemingly simple experience is a much bigger story involving identity, access, roles, permissions, devices, authentication, and security.
Before we can meaningfully detect suspicious behaviour or respond to incidents, we first need to understand what normal access should look like. Who is this person? What should they be allowed to do? Which device are they using, and should that device be trusted? Identity gives the rest of the security environment context.
In this series, we’ll pull back the curtain and explore how it all comes together as we build the security foundation for Wire Finance — our fictional organisation — beginning with identity and access.
Follow the Wire Finance Journey
Follow the chapters in order if you’re building along with Wire Finance, or jump directly to the topic you want to explore.
Welcome to Wire Finance
Meet Wire Finance and discover the environment we will build and secure throughout this journey.
What are we Building?
Discover how Wire Finance will evolve from an identity foundation into a connected security environment spanning endpoints, cloud, monitoring, detection, and incident response.
Company Profile
Meet the people, departments, technologies, and operating model that will shape every security decision inside Wire Finance.
Identity and Access Management
Wire Finance has people, departments, remote workers, cloud services, and sensitive data. Now we need to decide who gets access to what — and why.
Identity Lifecycle
Access should change when people do. Follow how Wire Finance manages identities as employees join, move through the organisation, and eventually leave.
Device Provisioning Model
Before a device can be enrolled, secured, or trusted, Wire Finance needs to decide what kinds of devices exist, who owns them, how they receive an identity, and how they move through the organisation.
Entra ID Implementation
The identity design is complete. Now we turn those decisions into a working Microsoft Entra ID environment for Wire Finance.
Endpoint and Device Management Implementation
Prepare Microsoft Intune and Windows Autopilot first, then build, register, deploy, and validate our first Wire Finance Windows 11 endpoint.
 Installing OpenCTI on Windows Ubuntu24.04